Open a laptop at the afterdeck table in the outer Tuamotu and the first negotiation may be with the light: tilt the screen, move it further into the shade, find the angle at which the words return. Digital privacy at sea involves a less visible negotiation. The inbox is familiar. So are the accounts, the permissions granted months ago and the small red notification that can draw the eye away from almost anything. The setting has changed considerably. The software has not.
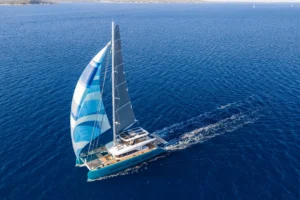
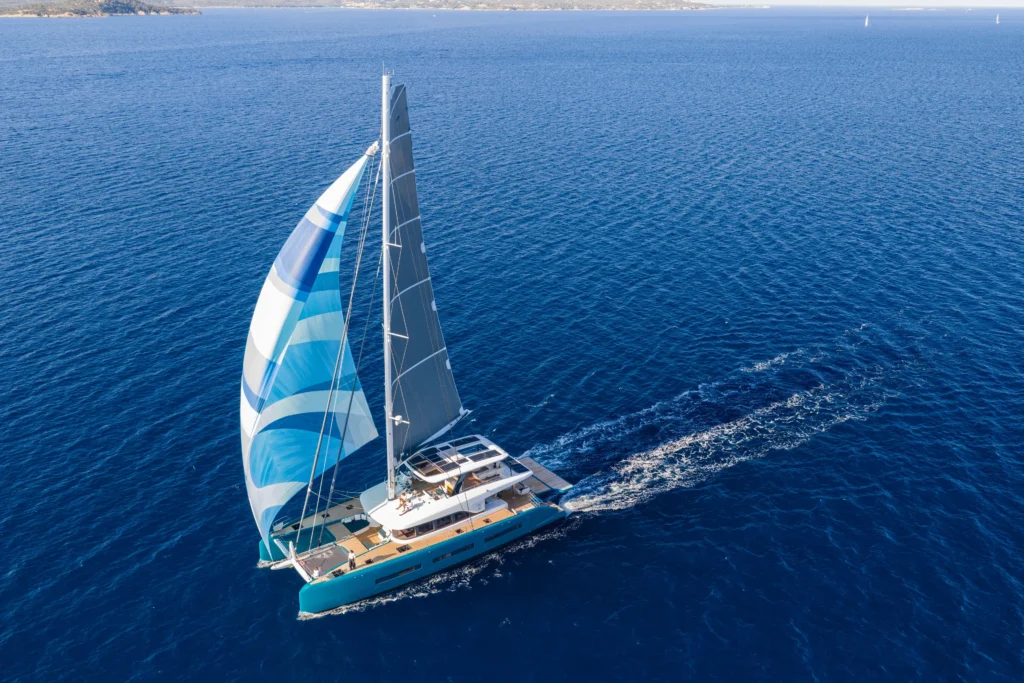
Aboard Discovery, the 2025 Lagoon Eighty2 sailing catamaran at the centre of Naora, Starlink maritime connectivity makes that working morning possible when service and conditions permit. An email can leave an atoll for an office far away. A conversation can continue across the Pacific. Neither possibility should be confused with a guarantee of uninterrupted access.
We should be equally precise about privacy. Sailing offshore does not retrieve information already collected, cancel the permissions on a phone or place a cloud account beyond the rules that govern it. What it can offer is room to examine those arrangements, and to stop treating every available connection as an instruction to connect.
What Your Digital Day Leaves Behind
The digital self is built partly from things we consciously provide: a name, a photograph, a delivery address, a message. Much of the rest comes from the ordinary operation of services. Signing in creates records. An application may collect device information, connection times and usage events. Location permissions may allow a more precise account of movement. Purchases and searches add another layer. None of this requires someone to be reading over your shoulder.
The distinction between content and metadata matters. Content is what a message says. Metadata is information around the exchange, potentially including the accounts involved and when it happened. The latter can reveal relationships and routines without revealing a sentence of the conversation. A recurring pattern may say more about a working life than any individual message.
Different organisations see different portions. The communications provider, the account provider, an advertiser and an employer managing a work device do not necessarily receive the same information. Some services share data with advertising partners or other recipients; some collect relatively little. Saying that everyone sees everything is inaccurate, and makes the practical decisions harder rather than easier.
A useful place to begin is with one account used every day. Review its signed-in devices, connected applications, location settings and retention controls. An old application may still have access long after its usefulness ended. An account export can make some retained information visible, although it will not necessarily expose every inference or downstream copy. Removing access can reduce future collection. It does not automatically erase the past.
This is also where privacy separates from security. A well-protected account may still collect more information than its owner wants. Preventing an intruder from entering and deciding what the service itself may retain are different jobs.
Digital Privacy At Sea And The Satellite Connection
Starlink changes the route by which information reaches the internet. It does not change the fundamental relationship between a person and the services they use. A message still reaches a messaging provider. A document saved to a company workspace still enters that company’s systems. The satellite connection is transport, not a private jurisdiction surrounding the boat.
Encryption protects different parts of this journey. An HTTPS connection normally encrypts the content travelling between a browser and the service it contacts. The internet provider should not ordinarily be able to read that protected content, though it can still observe connection information such as timing and data volume, and may learn or infer which services are being contacted. The service receiving the information can generally read what it needs to process unless another layer of encryption prevents it.
End-to-end encrypted messaging works differently: message content is protected between participating devices rather than merely on its way to a provider. That is valuable, but it does not protect against someone reading an unlocked phone, a recipient forwarding the message or every possible exposure through backups. The protection of stored copies depends on the system and its settings.
A VPN is another specific tool, not a universal answer. It creates an encrypted tunnel to the VPN provider and changes who can observe parts of the connection. Some trust moves from the local internet provider to the VPN operator. It does not stop an account identifying its signed-in owner, remove tracking within an application or make a compromised device safe. For company work, the appropriate arrangement is the one agreed with the company’s security team.
Data sovereignty therefore cannot be read from the chartplotter. Where information is stored, which organisations handle it, what contracts apply and which jurisdictions are involved remain relevant offshore. The position of Discovery is only one part of that picture. A sensitive document does not acquire different permissions because it was opened beside a lagoon.
The Accounts Worth Protecting First
The account that deserves attention first is often the primary email account, because it can receive password resets for many others. Protecting a dozen applications while leaving that recovery route weak is rather like checking cabin doors while forgetting the main entrance. The important question is what an intruder could gain next, not simply what is inside the first account.
Unique passwords stored in a reputable password manager reduce the damage when one service suffers a breach. Reusing a password allows a failure elsewhere to become your problem. The manager itself needs strong protection, and its recovery arrangements deserve attention before departure. A system that is secure only while one particular phone remains dry and charged is incomplete.
Multi-factor authentication adds another kind of evidence to a sign-in. Knowing a password and proving possession of a device are two distinct factors; entering two passwords is not. Where supported, passkeys and security keys offer resistance to phishing because authentication is bound to the genuine service. Authenticator codes are useful, but a code can still be surrendered to a convincing false sign-in page. An unexpected approval request should never be accepted simply to make the interruption disappear.
The offshore test is practical: imagine the phone is lost during a transfer ashore. Can the necessary accounts still be recovered without that phone receiving a text? Backup codes should be kept somewhere secure and accessible independently of the device they may need to replace. A photograph of them stored only on that same phone does not solve the problem.
Updates belong before departure too, with enough time afterwards to confirm that essential applications still work. On an employer-managed device, changes should stay within the organisation’s rules. The aim is dependable access with fewer weak points, not an improvised security overhaul on the morning of a passage.
The Work That Must Survive An Outage
A two-hour morning connection window can be a useful personal arrangement: answer what requires judgement, send what others need, then close the screen. It is not a property of the satellite service, nor a promise that the same hours will work every day. Heavy rain, equipment problems, obstructions and service restrictions can affect connectivity. A meeting involving someone who cannot tolerate delay needs a fallback that does not depend on the boat delivering a perfect connection.
In the Tuamotu, the timing of an atoll entrance may depend on the current through the pass, not the convenience of a calendar appointment. Wind and incoming swell can drive additional water into a lagoon, changing the outflow through its openings. A tidal prediction is therefore a starting point rather than a complete account of conditions. Sven, Naora’s founder and captain, plans every weather window and sails every leg himself. The demands of an approach take precedence over a call.
That need not make working aboard difficult. It makes preparation consequential. A document should be downloaded and opened before it is needed offline. A cloud icon is not evidence that the full file is on the device. Essential contact details and recovery information should also remain accessible without a live sign-in. For sensitive work, offline storage must follow the same rules that apply ashore.
Backups deserve the same distinction between appearance and function. Synchronisation keeps files aligned across devices, but may also reproduce an accidental deletion. The familiar backup principle is three copies, on two different types of storage, with one copy elsewhere. Its value is separation: a damaged laptop should not take the only backup with it. Encryption protects sensitive copies, while a test restoration establishes whether they are actually usable. A backup nobody has tried to recover remains an assumption.
The human preparation is just as important. Agree what constitutes an urgent matter and what can wait until the next connection. Give colleagues a clear expectation rather than leaving them to interpret silence. A bounded working day becomes easier when nobody has to guess whether you are unavailable, unaware or simply on the water.
Digital Privacy At Sea Is A Shared Practice
Privacy aboard is not only a relationship with distant companies. A photograph taken over dinner may reveal another person’s presence. An image shared without coordinates may still identify a location through its background or caption. Removing location metadata is worthwhile, but it does not make a photograph anonymous. Asking before sharing is often the more important act, particularly where children are involved.
The same discretion applies to work. Headphones prevent others from hearing the person on the call; they do not prevent anyone nearby from hearing your replies. A shaded table with a good signal may not be the right place for a confidential conversation. Privacy sometimes means choosing a different moment rather than adding another piece of software.
On a shared vessel, a locked screen is an ordinary courtesy, not an expression of suspicion. Notification previews can expose a message while its owner is elsewhere. Short automatic locking intervals and restrained previews reduce that possibility without making the device difficult to use. Someone should be able to sit down beside you without becoming an accidental reader of your correspondence.
The network deserves similar care. Confirm the guest connection with the crew rather than trusting a familiar-looking network name. From an operational perspective, guest internet access and the systems used to run the yacht should be treated as separate security concerns. That separation has to be established and checked, not inferred from the quality of the surroundings. Guests should never need to alter vessel equipment to solve a personal connection problem.
An Hour To Make The Abstract Specific
The Naora Circle session with a cybersecurity expert and digital rights professional is intended to bring these questions down to the scale of an actual device and an actual working life. Sixty minutes is enough to understand several consequential decisions. It is not enough to audit a business, certify a network or settle every question about cross-border data handling.
The useful conversation begins with particulars: which account controls recovery for the others, what remains accessible after a lost phone, what an employer permits abroad, what Starlink transports and what the applications collect. The objective is proportionate action. Someone responsible for confidential company information may need specialist advice beyond the session. Another person may discover that the most useful change is revoking access granted to an application they no longer remember installing.
There is no recording. That removes one persistent copy of the discussion; it is not a guarantee that words cannot be repeated or captured. The same principle needs to extend to automatic transcription and meeting assistants, which can create records even when nobody presses a recording button. Participants can discuss the shape of a problem without disclosing credentials, client identities or confidential documents. A private conversation still benefits from boundaries.
The Permission To Close The Screen
Naora’s world route is planned across five years, from 2027 to 2031. Members choose when they join, where along the route they step aboard and how long they stay. The yacht continues sailing. That freedom accommodates different relationships with work: a period with occasional calls, a longer passage requiring more preparation, or time deliberately kept clear. Nobody needs to perform disconnection to belong aboard.
After a swim, there is a physical interval before a screen becomes useful again: salt water on the fingers, a towel across the palms, the body cooling in the shade. The reflected light is still moving across the table. Opening the phone immediately is possible. Leaving it untouched for a little longer is possible too. The offshore setting does not make that decision for us, but it can make the decision visible.
Some messages carry genuine responsibility. A family member needs an answer; a colleague needs a decision that only you can make. Responding is not a failure to appreciate the place. The distinction lies in knowing why the screen is open, and being able to close it when that purpose is complete.
Privacy does not require every experience to be withheld. A photograph can be taken and sent with care. A conversation can be remembered without being transcribed. And there can be an unremarkable stretch of morning, with water beyond the shade, that remains with the people who were there.